SBS Password Manager: encrypted, identity-checked and audited credentials
Hosting logins, server passwords and client ERP credentials often sit in a shared passwords.xlsx that anyone with the link can read and nobody can audit. This module keeps them in Odoo against the project or employee, encrypted, revealed only after an identity check and logged.
Why teams install Password Manager
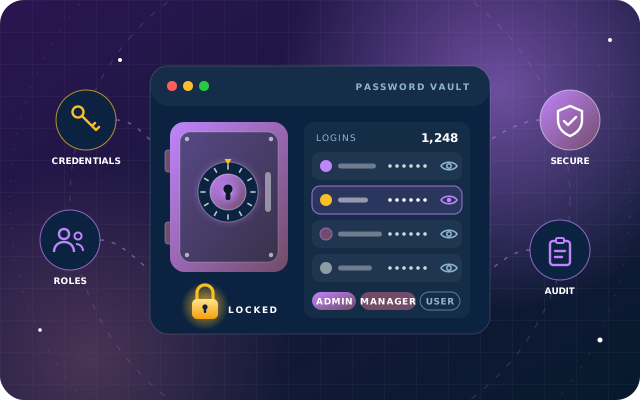
Every agency and IT team keeps a passwords.xlsx of hosting logins, domain registrar accounts, server root passwords and client ERP credentials - a file anyone with the share link can read, nobody can audit, and that gets copied to a laptop before a site visit. This module gives those credentials a home in Odoo, next to the project or employee they belong to, encrypted at rest with a key held outside the database, revealed only after an identity check to people on the record's visibility list, and logged every time someone looks.
Who it is for: Agencies and IT teams that hold hosting, domain, server, ERP and mail account credentials for their own projects, clients and employees and want them encrypted, access-controlled and audited inside Odoo 19 instead of a shared spreadsheet.
A database dump reveals nothing
Secrets are stored as Fernet ciphertext in a table no group can read, with the key held outside the database.
Only named people see passwords
Four roles plus a per-record Visibility list mean a credential is shown only to the people named on it, after they prove who they are.
A trail nobody can rewrite
Every reveal, copy, password change, import and export is written to an audit log that cannot be edited, deleted or created by hand.
What Password Manager adds to Odoo 19
Retire passwords.xlsx: encrypted credentials, identity-checked reveals, immutable audit
Fernet encryption at rest
Secrets are held in a separate table as Fernet ciphertext that no Odoo access group is allowed to read, and the record itself shows only a row of dots. When we inspected the column directly in PostgreSQL, it held only a Fernet token, 120 characters for a 20-character secret.
Key held outside the database
The encryption key lives in the Odoo configuration file or an environment variable, deliberately never in the database. Lose the key and the stored passwords cannot be recovered, by design.
Identity check before every reveal
Reveal raises Odoo's own identity check - your Odoo password - before anything is decrypted. Nothing is decrypted until you answer.
Credential panel with per-field copy
The panel holds the login, the address and the password, each with its own copy button. Copy writes from the value already in your browser, so nothing is decrypted twice.
Auto-hide and blur
The revealed value hides itself again after forty-five seconds and blurs if you switch away from the window.
Immutable audit log
Every reveal, copy, password change, import and export is logged, and so is every attempt that stopped at the identity check. Entries record who, what, which kind of secret, and when; editing, deleting or hand-creating one is refused.
Clipboard-confirmed copy logging
A copy is recorded only once the browser confirms the value reached the clipboard.
Four roles
Read-only, User, Manager and Admin. Only Admin may change Privacy, Visibility or Company on a saved record, run the encrypted import, or authorise a plaintext export.
Per-record visibility list
Each credential carries its own Visibility list; being a Manager does not make every password visible - you also have to be named on the record. A User Access List shows which credentials each person can actually reach.
Password history
Change Password moves the previous one into Old Password, still encrypted, so a rotation that breaks something can be traced.
Protected password field
On a saved record the password field is not editable, so an autofill cannot replace a working credential by accident.
Attached to projects and employees
Every credential belongs to a Project or an Employee you can already reach, so secrets sit next to the project or the employee they belong to.
Categories and search
PER, CORE, INTERNAL, CLIENT and OTHERS, each with its own menu, credentials grouped by category in the overview, and a search across item, entity, login and URL.
Encrypted import wizard
An admin-only wizard for CSV or spreadsheet files with a downloadable template; it encrypts the uploaded file before storing it, and the standard Odoo importer is blocked for these models.
Guarded export
Export needs the Admin role and a deliberate authorisation step before any secret leaves Odoo.
Key status page
The key page reports the encryption key's status without ever displaying the key itself.
Masked everywhere
Everything sensitive is masked until someone proves who they are; the password is never displayed on the form, and Reveal and Change Password sit under Credentials.
Tested on a live Odoo 19 Community database
We tested encryption at rest, masked display, the identity check on Reveal, copy-to-clipboard, password history, the immutable audit log and the admin-only privacy fields on a live database, and read the clipboard back in a real browser.
From install to everyday use
Install the module on Odoo 19 (tested on Community Edition) with the Employees (hr), Project (project) and Discuss (mail) apps in place.
Before first use, generate an encryption key, keep a recovery copy in your own secret manager, add the key to the Odoo configuration file or an environment variable, and restart Odoo; the key page then reports its status without displaying the key.
Give each person one of the four roles: Read-only, User, Manager or Admin.
Create a credential under one of the categories (PER, CORE, INTERNAL, CLIENT or OTHERS), attach it to the Project or Employee it belongs to, fill in item, entity, login and URL, and name the people on its Visibility list; the password is stored as Fernet ciphertext and shown as a row of dots.
Optionally bulk-load existing credentials with the admin-only encrypted import wizard, using the downloadable CSV or spreadsheet template.
To use a credential, press Reveal under Credentials, answer Odoo's identity check, then read or copy the login, address and password from the panel; it hides again after forty-five seconds.
Rotate a secret with Change Password; the previous value moves into Old Password, still encrypted.
Review the audit log to see who revealed, copied, changed, imported or exported what, and when, including attempts that failed the identity check; use the User Access List to see which credentials each person can reach.
When secrets must leave Odoo, an Admin runs the guarded export and completes the deliberate authorisation step.
What you will see in Odoo
- Credentials grouped by category. Everything sensitive is masked until someone proves who they are.
- The key page reports the encryption key's status without ever displaying the key itself.
- A credential. The password is never displayed on the form; Reveal and Change Password sit under Credentials.
- Pressing Reveal asks for your Odoo password first. Nothing is decrypted until you answer.
- The credential panel. Copy writes from the value already in your browser, so nothing is decrypted twice.
- The audit log, showing an attempt and the successful view that followed it.
SBS Password Manager explained
Hosting, domains, servers, ERP and mail accounts stored against a project or an employee. The secret is encrypted with a key that never touches the database, revealing one takes an identity check, and every look is written to a log nobody can edit.
You must configure an encryption key before first use. The key lives in your Odoo configuration file or an environment variable - deliberately never in the database. Lose the key and the stored passwords cannot be recovered. That is the point of the design, and it is your responsibility to look after it.
The database does not hold the password. Secrets are held in a separate table as Fernet ciphertext, and no Odoo access group is allowed to read that table. The record itself shows only a row of dots. We confirmed this at the storage layer: we saved a credential and inspected the underlying column directly in PostgreSQL. It held a Fernet token - 120 characters for a 20-character secret - and the plaintext did not appear anywhere in it. Reading the secret table through Odoo was refused outright with “No group currently allows this operation”.
Prove it is you, every time. Reveal raises Odoo's own identity check before anything is decrypted, then opens a panel holding the login, the address and the password - each with its own copy button. The value hides itself again after forty-five seconds, and blurs if you switch away from the window. Copy writes from the value already in your browser, so nothing is decrypted twice.
A log that cannot be tidied up. Every reveal, copy, password change, import and export is written to an audit log - and so is every attempt that stopped at the identity check. The log records who, what, which kind of secret, and when. A copy is recorded only once the browser confirms the value reached the clipboard. Immutable means immutable: we tried editing a log entry, deleting one and creating one by hand, and all three were refused - “Password audit logs are immutable” and “Password audit logs can only be created by the system”. The trail cannot be rewritten by the person who left it. Deleting a credential is not written to the audit log, so restrict who may delete accordingly.
Four roles and a per-record visibility list. Read-only may look at the credentials they are tagged on, and nothing more. User keeps their own credentials up to date. Manager looks after the team's credentials. Admin is the only role that may change Privacy, Visibility or Company on a saved record, run the encrypted import, or authorise a plaintext export. On top of the role, each credential carries its own Visibility list. Being a Manager does not make every password visible - you also have to be named on the record. When we tried to change Privacy, Visibility or Company as a non-admin, the change was refused.
We tested encryption at rest, the masked display, the identity check on Reveal, copy-to-clipboard, password history, the immutable audit log and the admin-only privacy fields on a live Odoo 19 Community database, and we read the clipboard back in a real browser to confirm Copy matched the revealed value. We have not yet tested the encrypted import wizard with a real file, plaintext export authorisation, or Copy on Safari or iOS.
Requirements and compatibility
Everything your Odoo administrator needs to know before installing SBS Password Manager.
- Technical name
sbs_password_manager- Odoo version
- 19.0, built and tested on Community Edition
- Price
- Free
- Hosting
- Odoo.sh, On Premise (not available on Odoo Online)
- Required Odoo apps
- Employees (hr), Project (project), Discuss (mail)
- Module dependencies
hr, project, mail- Access roles
- Read-only; User; Manager; Admin
Installation
Download SBS Password Manager from the Odoo App Store, or add it to your Odoo.sh repository or on-premise addons path.
In Odoo, activate developer mode, open Apps, choose Update Apps List and search for
sbs_password_manager.Install the module. Odoo installs the required apps listed above automatically.
Assign the access roles to the right users, then follow the configuration notes.
Configuration and requirements
- Generate an encryption key and keep a recovery copy in your own secret manager.
- Add the key to your Odoo configuration file or an environment variable - never in the database - and restart Odoo.
- Check the key page, which reports the key's status without displaying the key itself.
- Serve Odoo over HTTPS so the Copy button works; the browser clipboard API only runs on a secure origin.
- Assign the Read-only, User, Manager and Admin roles; only Admin can change Privacy, Visibility or Company on saved records, run the encrypted import, or authorise a plaintext export.
- Name the people who may see each credential on the record's own Visibility list.
- Restrict who may delete credentials, because deletions are not written to the audit log.
Odoo 20 or Odoo Enterprise? Check the Odoo App Store for the Odoo versions SBS Password Manager is available for. When we upgrade a database to Odoo 20 we port the SBS modules and other customisations it uses, and we implement Odoo Enterprise as well as Community. See what Odoo 20 changes.
Need help setting up SBS Password Manager?
The engineers who wrote SBS Password Manager can install it, configure it for your processes, extend it and support it. The module is free; you only pay for the help you choose.
- Installation on Odoo.sh or your own servers
- Configuration, data migration and user training
- Custom changes and integration with your other modules
- Support from the team that maintains the code
- Running Odoo Enterprise? We implement Enterprise too, and will tell you whether this module or a standard Enterprise app fits better
- Moving to Odoo 20? We port this module and your other customisations as part of the upgrade
Get help with Password Manager
Tell us about your Odoo setup and what you need. We reply within one business day.
Password Manager, answered
What happens if I lose the encryption key?
The stored passwords cannot be recovered; that is the point of the design. The key lives in your Odoo configuration file or an environment variable, never in the database, so before first use you generate one, keep a recovery copy in your own secret manager, add it to the configuration and restart Odoo.
Which Odoo apps does SBS Password Manager depend on, and where can it run?
It depends on Employees (hr), Project (project) and Discuss (mail). It is built for Odoo 19.0 and tested on Community Edition. It is available for Odoo.sh and on-premise installations, not Odoo Online.
Can an administrator read the passwords from the database?
Not from the database alone. Secrets are held in a separate table as Fernet ciphertext that no Odoo access group is allowed to read, and the key is kept outside the database, so a database dump or a direct SQL query shows only ciphertext. When we inspected the database directly in PostgreSQL we found only a Fernet token, and reading the secret table through Odoo was refused with 'No group currently allows this operation'. Anyone who can read the server's configuration file or environment can obtain the key, and the module's Admin role can authorise a plaintext export, so restrict both.
What is written to the audit log, and can it be edited?
Every reveal, copy, password change, import and export is logged, along with every attempt that stopped at the identity check, recording who, what, which kind of secret, and when. Editing, deleting or hand-creating an entry is refused: the logs are immutable and can only be created by the system. Deleting a credential is not logged, so restrict who may delete.
Why is the Copy button missing on my server?
Copy relies on the browser clipboard API, which browsers only allow on a secure origin. Over plain HTTP the button is hidden and the panel says so, leaving the value selectable to copy by hand. Serve Odoo over HTTPS if your team needs the button. We have not yet tested Copy on Safari or iOS.
Can Star Bit Solutions install and customise SBS Password Manager for us?
Yes. The engineers who wrote SBS Password Manager can install it on Odoo.sh or your own servers, configure it for your processes, extend it and support it. The module itself is free; you only pay for the implementation or support you choose. Call or WhatsApp +971 55 973 4524 or email info@starbitsolutions.com.
Put Password Manager to work in your Odoo.
Install it free from the Odoo App Store, or let our engineers deploy, configure and support it alongside the rest of your Odoo setup.